Subsequently it’s much completely different than different algorithms which work on Feistel Ciphering. Symmetric Key Cryptography also referred to as Symmetric Encryption is when a secret key is leveraged for each encryption and decryption functions. This methodology is the other of Asymmetric Encryption the place one secret is used to encrypt and another is used to decrypt. During this course of, data is converted to a format that cannot be read or inspected by anyone who doesn’t have the key key that was used to encrypt it.
Ema Report: Ssl/tls Certificate Security-management And Expiration Challenges
As the identical key’s used for ciphering and deciphering the data units, if the key is handed over to unauthorized malicious users, then the third events can easily intercept the info units. With a malicious person gaining access to the key, the entire system knowledge safety comes into question. Symmetric-key algorithms ought to be secure when used correctly and are extremely environment friendly, to permit them to be used to encrypt massive amounts of data without having a unfavorable effect on performance. In CBC mode, if the plaintext length isn’t a a quantity of of 128 bits, then the final block of plaintext shall be barely shorter than 128 bits. Then the XOR between the 128-bit previous ciphertext and the less-than-128-bit last block of plaintext could be undefined–bitwise XOR solely works if the 2 inputs being XORed are the identical length.
These devoted bodily devices forestall unauthorized entry by isolating keys from general methods and purposes. Our gadgets handle cryptographic operations, including key generation, rotation, and digital signature creation. This provides an additional layer of safety while bettering effectivity and compliance with industry standards.

Can Symmetric Encryption Be Broken By Quantum Computers?
- ” It may also be the case that the attacker had some partial details about the message \(M\) to start with.
- To fix these issues, the encryption algorithm can both be randomized or stateful—it both flips coins throughout its execution, or its operation depends upon some state data.
- However, securely sharing the vital thing between parties could be challenging, as its publicity compromises the safety of the encrypted info.
In CBC mode, the information leakage is contained, but in CTR mode, the leakage is catastrophic (equivalent to reusing a one-time pad). On the opposite hand, CTR mode may be parallelized, however CBC can not, which is why many excessive efficiency techniques use CTR mode or CTR-mode primarily based encryption schemes. From our encryption step, the last ciphertext block is just one hundred bits as an alternative of 128 bits. Then to retrieve the last one hundred bits of plaintext, all we now have to do is XOR the one hundred bits of ciphertext with the first 100 bits of the block cipher output and ignore the final 28 bits of block cipher output. Assuming trendy algorithms are used, the weak point within symmetric encryption is the symmetric key distribution. Another way to consider a symmetric secret is a shared secret, which means each side of the transaction has the same key.
Security
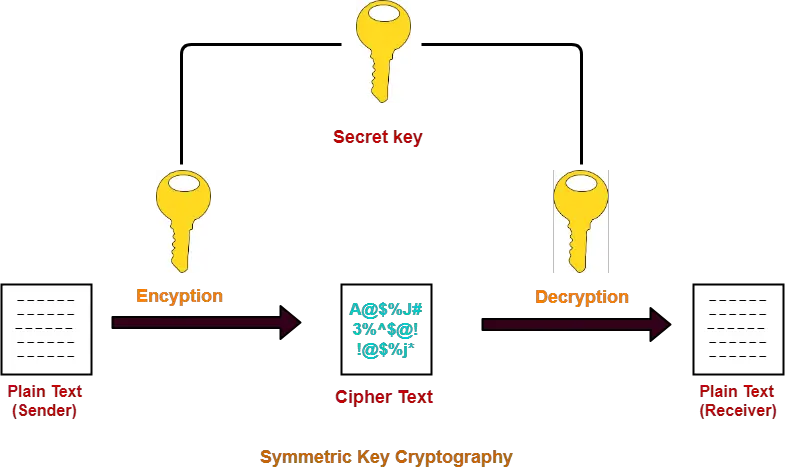
The main advantage of symmetric encryption over other ciphering strategies is its agility and efficiency for safeguarding a vast amount of sensitive knowledge. The symmetric algorithms provide a greater degree of security and the sheer simplicity can additionally be a logical advantage since there is a lesser want for processing powers. In Distinction To the DES, this tactic deploys two to 3 keys, enabling the algorithm to have multiple rounds of encryption and decryption processes. Triple Data Encryption Standard algorithm is far more secure than its predecessor- DES. In symmetric encryption, each the sending and receiving units have an analogous key, which is kept a https://alliancetac.com/security-training/onsite-courses/front-desk-security-course-outline secret.
The major distinction is the keys used for the encryption and decryption portions are totally different, thus the asymmetry of the algorithm. As the names imply, the general public secret is made out there to everybody, whereas the non-public key is kept secret. Which secret is used for encryption and which secret is used for decryption varies depending on the meant use of asymmetric-key algorithm in query. This time, we are ready to really XOR the a hundred bits of plaintext with the primary a hundred bits of block cipher output, and ignore the final 28 bits of block cipher output.

Begin Your Journey To Secrets-free Source Code
For example, with uneven encryption, when an email is encrypted using a public key, it might possibly only be decrypted by the recipient with the corresponding non-public key. Alternatively, when somebody signs a document with their non-public key, only the corresponding public key can be utilized for signature verification/authenticity. As we’ve simply seen, generating https://tsunamipump.com/category/blog/page/3/ new keys for each encryption is tough and costly.
Recent Comments